A significant 0-click vulnerability in the Pixel 6 modem stack was identified by Google’s Android Red Team and has since been patched. This vulnerability allows a skilled attacker to take control of a target’s Android device by making a call to the victim.
Four members of Google’s Android Red Team demonstrated how two Pixel modem vulnerabilities (CVE-2022-20170, CVE-2022-20405) could be combined to first hijack a targeted Pixel’s cellular modem communication to the second-generation (2G) wireless standard with the aid of a cheap $1,000 home-made cellphone base station during the Wednesday Black Hat session.
The aforementioned bugs were first found in 2021 by Android Red Team members. With a CVSS score of 9.8, both modem flaws are now classified as critical. The over-the-air remote code execution bug, designated CVE-2022-20170, was addressed in June 2022. An elevation of privilege (EoP) weakness was discovered in the second vulnerability, tracked as CVE-2022-20405, and it was fixed in August 2022. The EoP bug was deemed to be of moderate severity when it was initially discovered in an Android security bulletin.
If the attack is successful, the enemy will be able to wirelessly execute remote code that is running in the Pixel modem’s privileged context. According to experts, an attacker would then be able to conduct out assaults against the handset, such as launching a DoS attack, performing SMS/RSC (text message) sniffing and spoofing, MFA compromise, and enabling a hacker to switch to the device’s main operating system kernel.
Google claimed that it was not aware of the issues being used in the wild and that internal Alphabet procedures were to blame for the delay in disclosing the technical CVE information.
The Android Red Team at Black Hat includes Xuan Xing, Eugene Rodionov, Xiling Gong, and Farzan Karimi to demonstrate the assault (see image). Exploiting flaws in the Android Pixel’s cellular data connection to 2G networks is the initial attack vector.
The goal of this attack, according to Karimi, is to downgrade mobile devices to 2G.
The majority of modern cellular modems operate on 4G or 5G frequency bands. Yet, the majority of cellular data modem chipsets continue to support 2G and other dated wireless frequencies. For uncommon use scenarios including outdated wireless network geography, devices cycling down to save handset power consumption, and phones going to international markets where legacy 2G cellular networks are more prevalent, legacy support is required.
Weak encryption between towers and devices is one of the security vulnerabilities with 2G, which attackers may (and have) easily hacked in order to intercept conversations or text messages. Even current phones, according to researchers, occasionally transition to 2G to handle signal congestion, roaming, and network switching better.
The Android Red Team went above and beyond the examples of hackers and government enforcement utilizing fake base stations dubbed ISMI catchers (international mobile subscriber identity) or surveillance tools like Stingray to collect phone ID data, geolocation data, and content. They demonstrated how a vulnerable Pixel phone could be controlled remotely via a $1,000 home-built base station in addition to being used to collect data.
The Android Red Team went above and beyond the examples of hackers and government enforcement utilizing fake base stations dubbed ISMI catchers (international mobile subscriber identity) or surveillance tools like Stingray to collect phone ID data, geolocation data, and content. They demonstrated how a vulnerable Pixel phone could be controlled remotely via a $1,000 home-built base station in addition to being used to collect data.
“When a victim comes in proximity (a range of less than 5 miles) of the malicious base station it will connect to it,” said Karimi. “That allows the adversary to send the exploit payload and establish a foothold on the victim’s modem.”
In more precise terms, the RCE issue is an out-of-band (OOB) write error that happens during the decoding of OTA packets from 2G GSM connection. According to researchers, the EoP fault is caused by an error in the Pixel 6’s modem code, which renders memory space RWX (also known as the read (r), write (w), and execute (x) permissions) and available via signal processing instructions.
“The attacker fully controls up to 255 bytes written into 1-byte buffer in the heap,” researchers said. “CVE-2022-20170 enables us to overwrite heap header of the next adjacent chunk with fully controlled data.”
According to Google, the exploit technique allowed them to “corrupt nearby heap items and put a small amount of controlled bytes in the heap.” Uncertainty surrounds whether any of those items had an effect on the memory management unit (MMU) of the modem, which is essential to the next phase of the attack.
Researchers were able to execute 80 bytes of malicious shellcode via the modem’s (MMU) misconfiguration vulnerability (CVE-2022-20405), giving the attacker access to the affected device.
The 2G-attack method actually poses a threat. There have been reports of temporary 2G base stations popping up close to the hotels Paris Las Vegas and Caesars Palace during what is known as Hacker Summer Camp in Las Vegas, which features three security conferences: BSides, Black Hat, and DEF CON. Participants in DEF CON are renowned for having a habit of exposing cybersecurity experts who expose their digital equipment to a cyberattack.
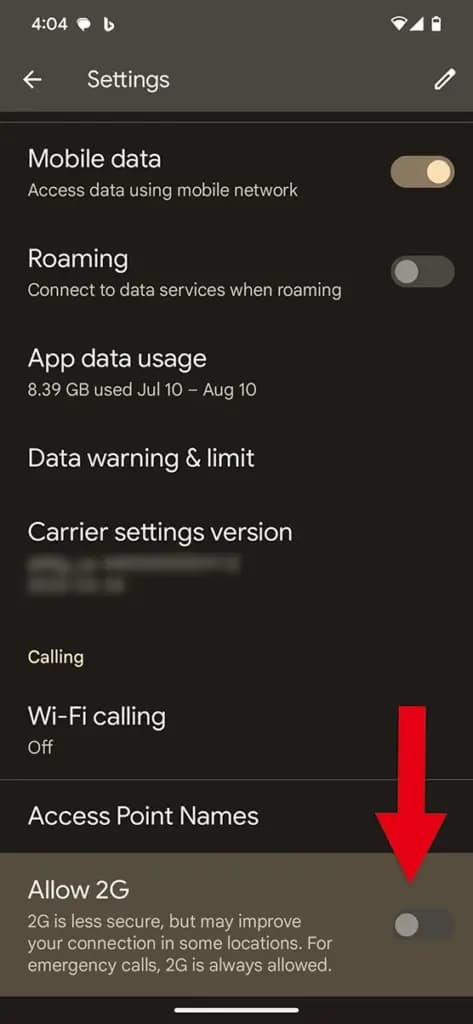
Researchers strongly advised Black Hat attendees to turn off 2G support on their phones. To turn off 2G capability, simply search for 2G in Settings on an Android device.
In related news, Google announced Tuesday a suite of Android 14 advanced cellular security mitigations for enterprises.
“Android 14 introduces support for IT administrators to disable 2G support in their managed device fleet. Android 14 also introduces a feature that disables support for null-ciphered cellular connectivity,” according to a Google Security Blog writeup.
Google Pixel Watch 5 (45mm)
Robert Haba is the founder and editor-in-chief of Droid Tools. A lifelong gadget enthusiast with over a decade following the Android ecosystem, he built this publication to cut through the noise and give readers honest, real-world coverage of the tech they actually use.
Bitdefender has discovered and analyzed a campaign dubbed Midnight Mimosa, in which malware comes preinstalled in the firmware of low-cost Android devices built on MediaTek platforms. The infection is persistent, runs as a pre-installed firmware system app, and can’t be removed through normal uninstall procedures. Anyone who switches on an affected device finds the malware […]
The Galaxy S27 Ultra display may avoid the compromises that held back its predecessor, according to a PhoneArena opinion piece. The writer cites an industry insider who said during a Q&A session on X (formerly Twitter) that Samsung is going to improve the display quality that suffered on the Galaxy S26 Ultra. What went wrong […]

WhatsApp is testing a new way to keep selected conversations off a person's linked devices, such as a laptop, tablet, or secondary phone. The company is expanding Advanced Chat Privacy with a new restriction that limits a chat to each participant's primary phone, and renaming the setting to Restricted Chat to make its purpose clearer. […]

Google built Pixel Search to save users from digging through their phone to find an app, email, photo, and more, and it now appears to be pushing that idea a step further by trying to figure out what to do with the results it surfaces. An APK teardown of Pixel Search version 1.0.983036833 by Android […]
The next story loads as you reach the end. You can also load it using the button.


Comments & Discussions
Join the conversation! We use Disqus to handle comments. Click the button below to load the comment section.