Skip to content
Droid Tools
Home
About UsContact
Editorial PolicyReview Policy
Privacy PolicyCookie PolicyTerms & Conditions
⌘K
Search
FacebookX (Twitter)InstagramThreadsBlueskyTikTokYouTubeRedditTelegramRSS Feed
Trending:
Galaxy S26•Pixel 10•Android 16•Nothing OS•Gemini AI•Smartwatches•Tech Deals•Latest Reviews•How-to Guides
Droid Tools

Droid Tools covers the latest Android news, device reviews, app updates, and OS guides. Stay informed with hands-on coverage from mobile tech experts.

Explore

  • News
  • Apps
  • OS
  • Phones
  • Reviews

Legal & Info

  • About Us
  • Contact
  • Editorial Policy
  • Review Policy
  • Privacy Policy
  • Terms & Conditions
  • Cookie Policy
  • Affiliate Disclosure
  • Disclaimer
  • HTML Sitemap
  • XML Sitemap
© 2026 Droid Tools. All rights reserved.
Home/News/NFC mobile payments are abused in the new Ghost Tap exploit to steal money.
News

NFC mobile payments are abused in the new Ghost Tap exploit to steal money.

Robert Haba
Nov 21, 20244 min read
Robert Haba
Robert Haba
Founder · Editor-in-Chief
Robert Haba is the founder and editor-in-chief of Droid Tools. A lifelong gadget enthusiast with over a decade following the Android ecosystem, he built this publication to cut through the noise and give readers honest, real-world coverage of the tech they actually use.
X
Profile →
NFC mobile payments are abused in the new Ghost Tap exploit to steal money.
0%
Share on XFacebookBluesky
Follow on Google
Advertisement
Trust this source on GoogleAlways see our reviews and tech guides first in search results
Add trusted source

Key Takeaways

Automated Editorial Synthesis
AI Overview
  • It also does not require constant victim interchange.
  • Ghost Tap was found by mobile security company Threat Fabric, which cautions about the growing potential and adoption of the novel method.
  • Threat Fabric told Droid Tools that it has recently observed an increase in the use of Ghost Tap in the field.

Cybercriminals have created a brand-new technique called “Ghost Tap,” which transmits NFC card information to money mules all around the world, to profit from stolen credit card information connected to mobile payment systems like Apple Pay and Google Pay.

The strategy expands on techniques used by mobile viruses such as NGate, which were reported by ESET in August and involved using payment card Near Field Communication (NFC) signals. Ghost Tap employs money mules at several remote places connecting with Point of Sale (PoS) terminals, is more obfuscated and difficult to detect, and does not require the victim’s mobile or card. It also does not require constant victim interchange.
Advertisement

Ghost Tap was found by mobile security company Threat Fabric, which cautions about the growing potential and adoption of the novel method. Threat Fabric told Droid Tools that it has recently observed an increase in the use of Ghost Tap in the field.

An overview of Ghost Tap and a comparison with NGate

The attack starts by stealing payment card information and intercepting the one-time passwords (OTP) required to register for a virtual wallet on Google Pay and Apple Pay. Payment card information can be stolen via phishing websites, keylogging, or banking malware that shows overlays that seem like digital payment apps.

Malware that tracks text messages or social engineering are two ways that OTPs can be stolen. Previously, NGate-based assaults required the use of specialist software to mislead the victim into scanning their card via the NFC mechanism on their device.

Advertisement

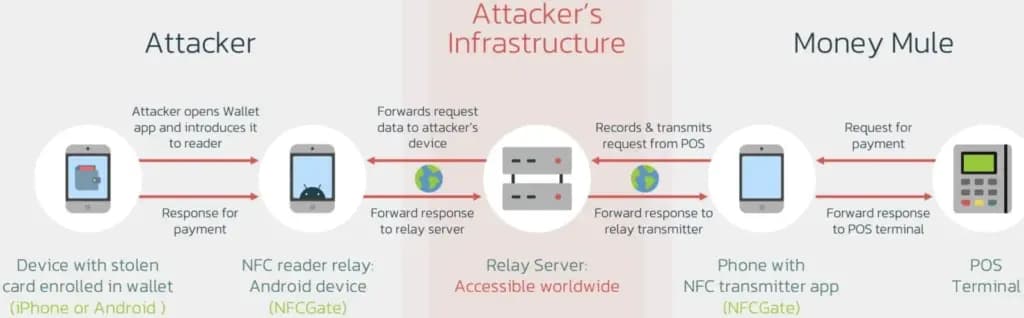
Payment card information is still transmitted using the NFCGate tool. But in the interim, a relay server is set up to transmit the information to a vast network of money mules while hiding their true locations. Using the NFC chip on their cellphone, the mules then make large-scale, multi-location retail purchases, making it challenging to identify the main attacker or map the fraud network.

You May Also Like
Recommended
1

Huawei Kirin 9050 Pro chipset: full specs and what’s new

kirin 9050
2

The 5 biggest phone launches to watch in September 2026

semptember 2026 phones
3

Google’s Scam Detection could be coming to Xiaomi phones, teardown suggests

Threat actors were restricted to making minor contactless payments and ATM withdrawals during the NGate attacks, which jeopardized their identity and occasionally resulted in arrests.

The threat actors have stopped making ATM withdrawals as a result of the new Ghost Taps operation. Rather, they merely carry out cash outs at the time of sale and distribute them around a vast global network of mules. This just endangers the mules by obscuring the path to the primary perpetrators of the nefarious conduct.
Defending Against Ghost Tap

Threat Fabric cautions that because the transactions seem authentic and take place across several locations, the new strategy is difficult for financial institutions to identify and halt.

Advertisement

The researchers claim that although many banks’ anti-fraud systems identify purchases made in odd places, as when visiting another nation, the many tiny payments might evade these detections.

“The new tactic for cash-outs poses a challenge for financial organisations: the ability of cybercriminals to scale the fraudulent offline purchases, making multiple small payments in different places, might not trigger the anti-fraud mechanisms and might allow cybercriminals to successfully buy goods that can be further re-sold (like gift cards),” explains ThreatFabric.

If the attack is used widely, the total amount lost might be substantial even though all of these tiny transactions seem to have originated from the same device (connected to the same Apple Pay or Google Pay account). The mules switched their handsets to “airplane mode,” which still permits the NFC system to operate normally, in order to avoid being tracked.

Banks may only prevent Ghost Tap by flagging transactions made using the same card at locations that are physically impossible to visit in between charges. For instance, carrying out a fraudulent transaction in Cyprus 10 minutes after completing one in New York.

From the standpoint of the customer, keeping an eye out for fraudulent transactions and promptly reporting them to your bank is essential for freezing the card and reducing losses.
Trust this source on GoogleAlways see our reviews and tech guides first in search results
Add trusted source
Tags:#android#cybersecurity#exploit#ghost#nfc#payments#security
Recommended Deals
1 / 5
Google Pixel Watch 5 (45mm)

Google Pixel Watch 5 (45mm)

5.0
529.99
Buy on Amazon
💎Best Android Device
Samsung Galaxy S26 Ultra

Samsung Galaxy S26 Ultra

4.9
$1,212.85$1,499.99-19%
Buy on Amazon
✨DEAL
Google Pixel 11 Pro

Google Pixel 11 Pro

5.0
1,099.00$1,299.00-15%
Buy on Amazon
Samsung Galaxy Watch 8

Samsung Galaxy Watch 8

4.9
$289.99$349.99-17%
Buy on Amazon
👑A good choice
Apple iPhone 17 Pro

Apple iPhone 17 Pro

4.8
$1,012.97$1,099.00-8%
Buy on Amazon
* As an Amazon Associate, Droid Tools earns from qualifying purchases. Read our editorial policy
Robert Haba
Robert HabaFounder · Editor-in-Chief
X

Robert Haba is the founder and editor-in-chief of Droid Tools. A lifelong gadget enthusiast with over a decade following the Android ecosystem, he built this publication to cut through the noise and give readers honest, real-world coverage of the tech they actually use.
Advertisement

Comments & Discussions

Join the conversation! We use Disqus to handle comments. Click the button below to load the comment section.

Advertisement

Latest Stories

Google Messages rolls out Keep Notes integration from the September Android Drop
01

Google Messages rolls out Keep Notes integration from the September Android Drop

02

Honor MagicOS 11 debuts September 15 with Glazed Architecture, faster YOYO

03

OnePlus 16 reservations open in China, revealing design and colors ahead of launch

04

Honor MagicOS 11 to debut with hidden Power Saving Suggestions feature

Advertisement
Amazon Deals
5.0
Google Pixel Watch 5 (45mm)

Google Pixel Watch 5 (45mm)

Best Price
529.99
Buy

Top Deals

Pixel Watch 5 vs. Pixel Watch 4: what actually changed

Deal
Pixel Watch 5 vs. Pixel Watch 4: what actually changed

Apple Watch Series 12 vs Pixel Watch 5: how they compare

Deal
Apple Watch Series 12 vs Pixel Watch 5: how they compare

Garmin Epix Pro Gen 2 Sapphire Edition drops to under $700 at Amazon

Deal
Garmin Epix Pro Gen 2 Sapphire Edition drops to under $700 at Amazon
Advertisement
Advertisement
Recommended stories

Continue reading

More from this category →
kirin 9050
NewsSep 11, 2026

Huawei Kirin 9050 Pro chipset: full specs and what’s new

Huawei has released its new high-performance Kirin 9050 Pro chipset, and details about the silicon's architecture are now available across CPU, GPU, NPU, modem, security, and cooling. CPU, GPU, and NPU upgrades The chip's LinxiCore CPU supports simultaneous multi-threading and delivers a 24% gain in peak single-core performance alongside a 52% gain in multi-core concurrent […]

By Robert Haba
semptember 2026 phones
NewsSep 8, 2026

The 5 biggest phone launches to watch in September 2026

September is usually iPhone season, but this year several Android brands are packing their very best hardware into the same four-week stretch, aiming to steal some of the spotlight. More than 20 phones are expected to launch this month alone, and here's a rundown of five of the biggest phone launches on the calendar for […]

By Luiza Mosneagu
NewsSep 4, 2026

Google’s Scam Detection could be coming to Xiaomi phones, teardown suggests

Google's Scam Detection feature could be coming to Xiaomi phones next, according to a new APK teardown by Android Authority. The AI-powered scam-call warning tool debuted first on Pixel devices, has since expanded to Samsung's Galaxy S26 series, and has shown signs of heading to vivo phones as well, and Android Authority now says it's […]

By Robert Haba
android-trojan
NewsSep 4, 2026

New StreamRat Android banking trojan spreads via fake streaming ads

Cybersecurity researchers at ThreatFabric have disclosed a new Android banking trojan called StreamRat that was pushed to Spanish-speaking users through a fake television-streaming campaign on Meta and can hand its operators near-complete control of an infected device. According to ThreatFabric, the campaign's advertising focused on Spain and reached an estimated 570,950 Meta accounts in the […]

By Robert Haba
Next in queue

Read the next article

The next story loads as you reach the end. You can also load it using the button.