Using a warning to backup the key to prevent losing access, a recently identified Android malware known as Crocodilus deceives users into entering the seed phrase for the bitcoin wallet.
Despite being a recent banking malware, Crocodilus has fully functional capabilities to remotely control, take over the device, and collect data.
According to researchers at the fraud prevention firm ThreatFabric, the malware is disseminated by a custom dropper that gets around security measures in Android 13 and later.

The dropper circumvents Accessibility Service limitations and installs the virus without activating Play Protect.
Crocodilus is unique because it uses social engineering to force victims to divulge their crypto-wallet seed phrase.
A screen overlay alerting users to “back up their wallet key in the settings within 12 hours” or risk losing your wallet is how it accomplishes this.
“This social engineering trick guides the victim to navigate to their seed phrase (wallet key), allowing Crocodilus to harvest the text using its Accessibility Logger,” ThreatFabric explains.
“With this information, attackers can seize full control of the wallet and drain it completely,” the researchers say.
Crocodilus was seen to target customers in Spain and Turkey, including bank accounts from those two nations, during its initial operations. Based on the debug messages, it seems that the infection originated in Turkey.
Although the exact mechanism of the first infection is unknown, users are usually duped into downloading droppers by malicious websites, phony SMS or social media advertisements, and third-party app shops.
When Crocodilus is launched, it has access to Accessibility Services, which are typically designated for helping individuals with disabilities. These services allow Crocodilus to make navigation motions, monitor for app launches, and unlock screen content.
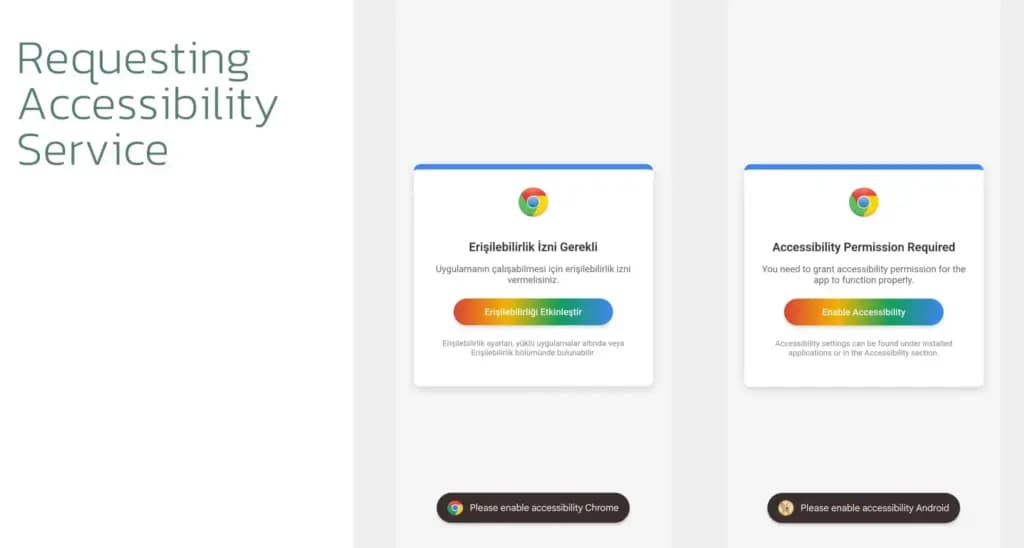
Crocodilus puts a phony overlay over the legitimate app when the victim accesses a targeted banking or cryptocurrency app in order to obtain the victim’s login information.
The bot component of the malware supports a set of 23 commands that it can execute on the device, including:
Additionally, the malware has remote access trojan (RAT) capabilities that let its operators swipe, tap, and browse the user interface, among other things.
To collect one-time password codes used for two-factor authentication account protection, a specific RAT command is also available to snap a screenshot of the Google Authenticator application.
To conceal the activity from the victim and give the impression that the device is locked, Crocodilus operators can mute the device and activate a black screen overlay while doing these tasks.
Crocodilus may soon expand its activities and add more apps to its target list, even if it currently seems to be targeting only Spain and Turkey.
It is recommended that Android users make sure Play Protect is constantly enabled on their devices and refrain from downloading APKs from sources other than Google Play.
Google Pixel Watch 5 (45mm)
Robert Haba is the founder and editor-in-chief of Droid Tools. A lifelong gadget enthusiast with over a decade following the Android ecosystem, he built this publication to cut through the noise and give readers honest, real-world coverage of the tech they actually use.

Cybersecurity researchers at Huntress have uncovered a campaign where hackers built a custom ChatGPT model to trick people into launching malware on their own PCs, turning one of OpenAI's own features against its users. The campaign starts on Google search. Anyone searching for “chatgpt” might click a sponsored ad at the top of the results […]

Huawei has released its new high-performance Kirin 9050 Pro chipset, and details about the silicon's architecture are now available across CPU, GPU, NPU, modem, security, and cooling. CPU, GPU, and NPU upgrades The chip's LinxiCore CPU supports simultaneous multi-threading and delivers a 24% gain in peak single-core performance alongside a 52% gain in multi-core concurrent […]
September is usually iPhone season, but this year several Android brands are packing their very best hardware into the same four-week stretch, aiming to steal some of the spotlight. More than 20 phones are expected to launch this month alone, and here's a rundown of five of the biggest phone launches on the calendar for […]
Google's Scam Detection feature could be coming to Xiaomi phones next, according to a new APK teardown by Android Authority. The AI-powered scam-call warning tool debuted first on Pixel devices, has since expanded to Samsung's Galaxy S26 series, and has shown signs of heading to vivo phones as well, and Android Authority now says it's […]
The next story loads as you reach the end. You can also load it using the button.

Comments & Discussions
Join the conversation! We use Disqus to handle comments. Click the button below to load the comment section.