
Android users installing apps from third-party app stores are at risk of the BlackRock malware. How can this malware be stopped?
BlackRock malware is yet another threat worrying Android users. This newly-discovered malware can target a variety of different applications, thereby stealing your information.
Make sure you know what BlackRock malware is, and how you can protect yourself, before installing another file.
Security firm, ThreatFabric, discovered a digital danger that affects Android devices in May 2020: BlackRock malware.
Analysts however quickly discovered that BlackRock malware is not really a new threat. BlackRock malware is the product of leaked source code for Xeres malware, which is a form of trojan LokiBot banking.
Despite the fact that BlackRock malware is based on a banking trojan, it does not just affect banking apps. It also targets applications for shopping, leisure, social relations, entertainment and even dating. This extensive publicity makes it extremely risky.
It currently has 337 apps on its goal list, some of which you might be using on a regular basis. Its target applications aren’t limited to one country either — it targets applications across Europe, North America , and Australia.
ThreatFabric presents the full list of targets in its article. Some of the applications on the list include Gmail, Netflix, Snapchat, eBay, Twitter, TikTok, PayPal and more.
BlackRock malware has not been detected on the Google Play Store until now. Currently it targets downloaded apps from third-party sites, but that does not mean that BlackRock malware will never appear on the Google Play Store. Aggressive hackers also can find ways to break Google’s protection protocols.
When BlackRock malware appears on your computer it can never be noticed by an unknowing user. It uses a technique known as a “overlay,” a fake window which pops up over a legitimate app. The overlay mixes with the software so it’s hard to say whether the pop-up is part of the app or not.


The window will ask you to enter your credit card number and login code, before you can even start using the legal app. This helps it to get the details right off the bat.
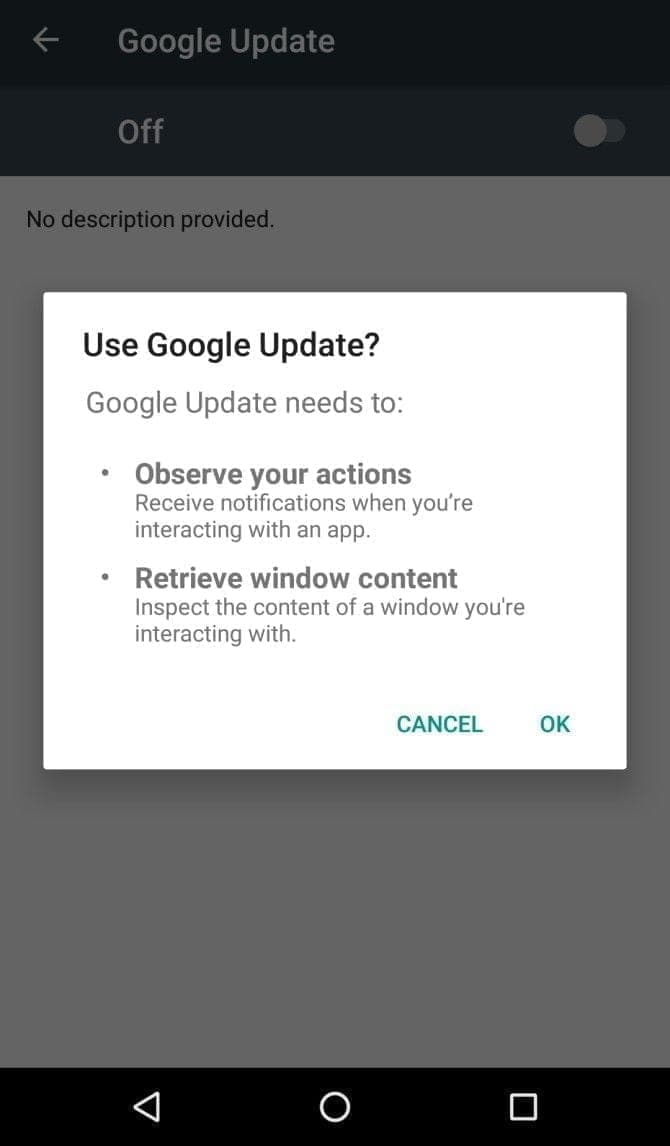
It infiltrates your device in the first place by getting Accessibility Services permissions. When you install an infected app, it’ll prompt you to enable a fake Google Update. Accepting the “Google Update” allows it to intervene with your device.
If you aren’t familiar with an Android’s Accessibility feature, you should know that it’s one of the most powerful functions on your device. It’s meant to help Android owners with disabilities, but Accessibility Services can be used to hack your phone as well. This feature can automate a variety of tasks for the user, including tapping the screen, reading text aloud, and even creating captions.
Giving BlackRock permission to use Accessibility Services lets you build the overlay that you can see when you open the target app. It also gives additional functionality to the malware, as it can then use an Android DPC (device policy controller) to grant administrator privileges to itself.
In other words, it not only steals the confidential details you type into its overlay — it can actually do a lot more than that. BlackRock does not only intercept SMS messages, mask alerts and lock your computer, it can also engage in keylogging. That said, this malware is certainly not what you want on your computer.
As mentioned earlier, the Google Play Store still hasn’t found BlackRock. But just because apps from third-party app stores are currently being targeted, that doesn’t mean it’ll never make its way to Google Play.
ThreatFabric notes that it “can not yet predict how long BlackRock will be active on the threat landscape.” Meanwhile, it’s necessary to bear in mind some precautions before installing apps.
It’s not a bad idea to have an antivirus app on your smartphone, but unfortunately, an antivirus app won’t stop the BlackRock malware. When BlackRock infiltrates your phone, it has a feature that blocks you from using an antivirus app.
As soon as you open an antivirus or an Android cleaner app, such as Avast, Kaspersky, McAfee, BitDefender, or Superb Cleaner, BlackRock will immediately redirect you to your Home screen. This prevents you from removing the malware using an antivirus app.
So, if you download a sketchy app from a third-party store, and think that an antivirus app will keep you safe from all threats, think again.
No matter how legit an app may seem, you should keep an eye on the app permissions. Some apps request permissions that have nothing to do with the App’s core function.
For example, your SMS messages obviously don’t need access to a flashlight app. This is a sign that you should immediately uninstall the App.
As BlackRock malware asks for permissions from Accessibility Services, you’ll want to look for any apps that require that particular privilege. If an app is legitimately for users with disabilities, has good reviews, and is from the Google Play Store, you are likely to have confidence in granting permission to the accessibility services. If not, avoid giving that privilege to any applications that don’t need it.
Google Play Protect was put in place to scan your installed apps for malware as soon as you download them, as well as scan them periodically once installed. Third-party app stores don’t have this safety feature, so you’re pretty much on your own in terms of security.
The lack of security protocols on third-party stores has allowed BlackRock malware to thrive. To lower your risk of encountering BlackRock malware, try to avoid third-party apps stores, and refrain from downloading APKs.
BlackRock malware will hopefully never hit the Google Play Store. There really isn’t any telling if the actors behind BlackRock malware can find a loophole in Google’s security policies, but if they succeed, BlackRock malware could accumulate a significant number of victims.
If BlackRock ever reaches the Google Play Store, it’s not too surprising. After all, despite Google’s strict security protocols, several apps that contain Joker malware still managed to make their way onto the Google Play Store.
Google Pixel Watch 5 (45mm)
Cristian Penisoara is a Guides Writer and Android specialist at Droid Tools. An Android user since version 2 and a professional event photographer, he combines technical curiosity with a detail-oriented approach - every guide he publishes is tested step-by-step on a real device before it goes live.
You can block ads on Android more effectively by pairing Brave’s Aggressive Shields setting with the system’s Private DNS feature. The setup filters ads at both the browser and system levels, takes only a few minutes to configure, and avoids the battery drain and VPN conflicts that come with dedicated ad-blocking apps. Why one ad […]

Behind a two-tap recharge sits a surprising amount of plumbing. Every prepaid network has its own rules about what can be topped up, in which denominations, and how quickly credit posts to a SIM. MobileTopUP hides that complexity behind a single form: pick a country, enter a number, choose an amount. What the coverage map actually covers […]
Knowing how to turn off Safe Mode on Android comes in handy, since Safe Mode is a built-in troubleshooting tool that disables every third-party app on a phone and switches on Airplane Mode, making it easier to isolate an app causing lag, battery drain, or other issues. It's also useful for safely deleting a suspected […]
Opening a brand-new phone has a particular excitement. After removing the plastic, you move your pictures, log into your Google account, and begin taking your first snapshot. However, we frequently overlook a few crucial settings that can improve our phone in all that excitement. I looked at a few options on my current phone, a […]
The next story loads as you reach the end. You can also load it using the button.


Comments & Discussions
Join the conversation! We use Disqus to handle comments. Click the button below to load the comment section.