The foundation of Public Key Infrastructure (PKI) is its root certificates, which are certified by reputable Certificate Authorities, or CAs. A pre-packaged root store seen in browsers, apps, and other programs serves as a trust seal for these certificates. A website that supports HTTPS but isn’t using a certificate signed by a CA in the root store of your browser will be marked as insecure when you visit it. Applications and browsers can frequently update their certificates, but unless you use an OTA update, your phone cannot. According to Esper, with Android 14, that might alter.
Due to our reliance on certificates as the foundation of a chain of trust when visiting websites, there have been a few scares involving them throughout the years. Let’s Encrypt, a nonprofit CA, has signed the certificate used here on XDA. Your connection to this website is safe and secure thanks to their certificate, which was signed by the Internet Security Research Group. The same holds true for any other HTTPS-enabled website you visit.
Every operating system has its own built-in root store, and Android is no different. You can actually view this root store on your Android smartphone by navigating to security and privacy in your device’s settings. From there, it will depend on the type of device you’re using, but the screenshots below show where it is on OneUI 5.
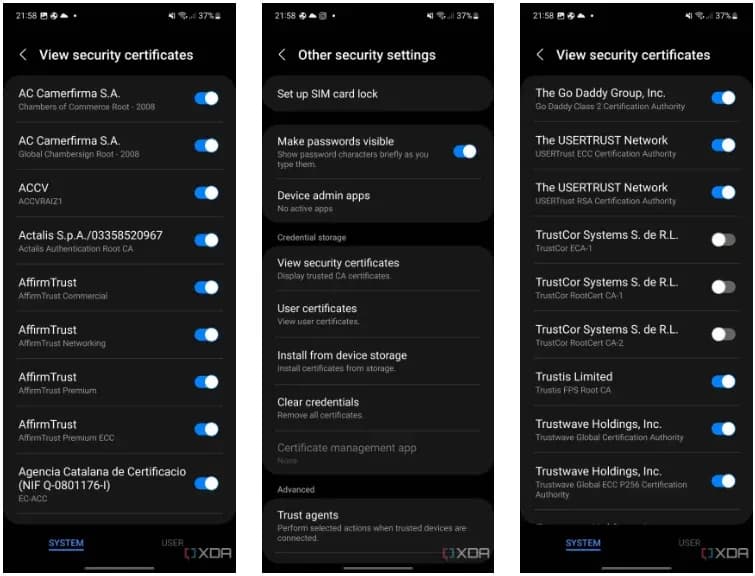
But even this root shop isn’t the be-all and end-all, you know? In an effort to fend off Man-in-the-Middle (MITM) attacks, apps can choose to utilize and trust their own root store (like Firefox does) and they can accept only particular certificates (a practice known as certificate pinning). Users can install their own certificates, but since Android 7, app developers have had to agree to let their apps utilize these certificates.
A large portion of the internet depends on the security of the Internet Security Research Group since Let’s Encrypt certificates are cross-signed by this organization. The ISRG would have to revoke the key if it lost control of its private key (should it be stolen, for instance). Depending on how businesses react, some portions of the internet may become inaccessible to hardware lacking an updateable root certificate. Even though it’s a completely improbable nightmare scenario, Google aims to prevent situations like that from happening. Because of this, what is happening with TrustCor right now might be telling Google that it’s time to give Android updatable root certificates.
As an example, academics have questioned TrustCor after discovering that company allegedly has close ties to a US military contractor. Although TrustCor still has access to its private key, many businesses that must choose which certificates to include in their root stores no longer trust the company. These researchers said that TrustCor, a contractor for the US military, had paid programmers to include malware that gathered data from smartphone apps. Faith is crucial in PKI, but after these claims surfaced, TrustCor lost that trust. Since then, TrustCor has been abandoned as a certificate authority by organizations like Google, Microsoft, and Mozilla. But even though the commit has already made, an OTA update will be necessary to remove TrustCor’s certificates from the Android root store.
The upside is that you can disable TrustCor’s certificates on your device now by going to your certificates on your device, as we showed above, and then scrolling to TrustCor and disabling the three certificates that come with your device. According to developers from the GrapheneOS project, there should be “very little impact on web compatibility due to this CA barely being used by anyone other than a specific dynamic DNS provider.”
If you’re familiar with Project Mainline, then you can already see how this can help solve the problem. Google makes use of Mainline modules which are delivered through the Google Play Services framework and the Google Play Store. Each Mainline module is delivered as either an APK file, an APEX file, or an APK-in-APEX. When a Mainline module is being updated, the user sees a “Google Play System Update” (GPSU) notification on their device. Effectively, to deliver updates to critical components, Google has bypassed the need to wait for an OEM to roll out an update, choosing to do the task itself. Bluetooth and Ultra-wideband are two essential Mainline modules handled by Google.
Conscrypt, a Mainline module that provides Android’s TLS implementation, will allow updatable root certificates in a future release, according to changes on the AOSP Gerrit (found by Esper). In the event that a situation similar to TrustCor (or worse) arises in the future, this would mean that certificates may be removed (or even added) via a Google Play System Update through Project Mainline, ensuring a considerably speedier process. It’s unclear when this will launch, but Android 14 is probably going to get it. Technically, Google could launch it with Android 13 QPR2, but it would only help Google Pixel users until Android 14 is released to the rest of the world next year. This is due to the fact that other OEMs usually do not release QPR updates.
The entire reason for this to exist would be so that Google can maintain control over another crucial aspect of device security without needing to rely on OEMs pushing updates instead. An OTA is currently required to update certificates, but in an emergency situation, every day where users don’t have an update could matter. Utilizing Project Mainline to ensure that users can get crucial certificate updates in time if they’re ever needed is certainly a welcome change.
Google Pixel Watch 5 (45mm)
Robert Haba is the founder and editor-in-chief of Droid Tools. A lifelong gadget enthusiast with over a decade following the Android ecosystem, he built this publication to cut through the noise and give readers honest, real-world coverage of the tech they actually use.
Bitdefender has discovered and analyzed a campaign dubbed Midnight Mimosa, in which malware comes preinstalled in the firmware of low-cost Android devices built on MediaTek platforms. The infection is persistent, runs as a pre-installed firmware system app, and can’t be removed through normal uninstall procedures. Anyone who switches on an affected device finds the malware […]
The Galaxy S27 Ultra display may avoid the compromises that held back its predecessor, according to a PhoneArena opinion piece. The writer cites an industry insider who said during a Q&A session on X (formerly Twitter) that Samsung is going to improve the display quality that suffered on the Galaxy S26 Ultra. What went wrong […]

WhatsApp is testing a new way to keep selected conversations off a person's linked devices, such as a laptop, tablet, or secondary phone. The company is expanding Advanced Chat Privacy with a new restriction that limits a chat to each participant's primary phone, and renaming the setting to Restricted Chat to make its purpose clearer. […]

Google built Pixel Search to save users from digging through their phone to find an app, email, photo, and more, and it now appears to be pushing that idea a step further by trying to figure out what to do with the results it surfaces. An APK teardown of Pixel Search version 1.0.983036833 by Android […]
The next story loads as you reach the end. You can also load it using the button.


Comments & Discussions
Join the conversation! We use Disqus to handle comments. Click the button below to load the comment section.